DNS analysis joins Red Hand Analytics
A dedicated DNS workspace surfaces resolvers, noisy clients, unresolved requests, conflicting answers, and unusual DNS data exchange.
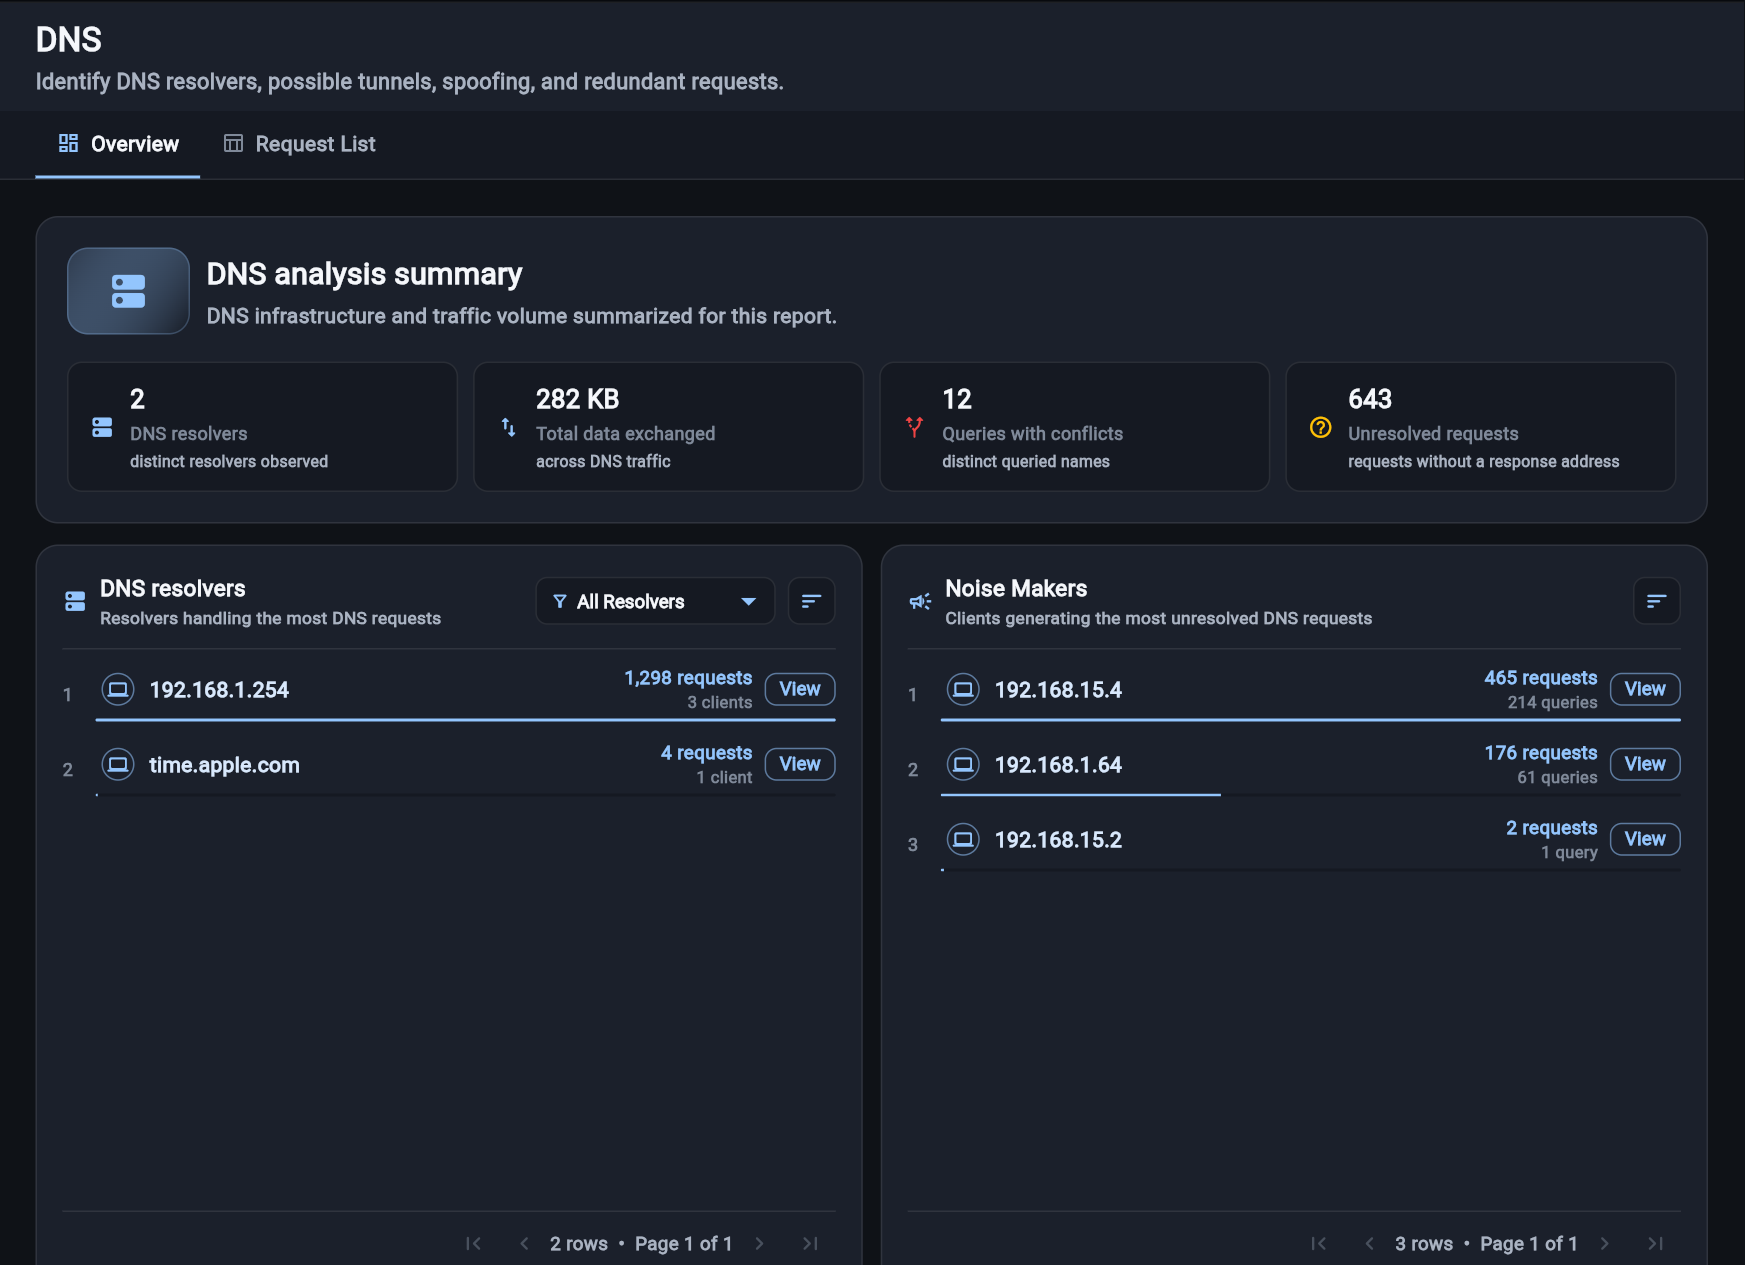
DNS now has a dedicated analysis workspace instead of being visible only through general activities and connections.
What changed
The overview surfaces the DNS resolvers observed in the report, clients generating unresolved requests, queries with conflicting answers, and client-domain pairs moving the most data through DNS requests.
Each result remains connected to its underlying DNS requests. Opening View applies the relevant client, resolver, domain, or conflict criteria to the Request List so the evidence can be reviewed without rebuilding the filter manually.
More context where it matters
Domains can open threat-intelligence context without leaving the DNS workflow. Request rows keep query, response, initiator, resolver, timing, and upload/download information together for faster comparison.
Where to find it
Open the sample DNS analysis, or read the DNS documentation.
See it for yourself